|
Bureau Veritas 攜手勤業眾信 協助磐儀成功取得
IEC 62443-4-1 證書
強化安全產品開發生命週期,提升全球產品資安競爭力
工業電腦與邊緣運算設備加速走向連網與智慧化,產品資安也不再只是單一功能或系統的防護,而是從設計、開發、測試到後續維護,都必須納入產品生命週期的重要考量。對於布局全球市場的製造商而言,如何從研發源頭建立安全機制,並透過國際標準驗證安全開發能力,已成為提升客戶信任與市場競爭力的重要關鍵。
Bureau Veritas(必維國際檢驗集團)完成磐儀科技(ARBOR Technology)IEC 62443-4-1 Secure Product Development Lifecycle(安全產品開發生命週期)驗證,並正式取得 IEC 62443-4-1 ML2 證書,展現磐儀科技持續強化產品資安與安全開發流程的投入,並進一步提升面對全球產品資安規範及市場要求的能力。
|
|
|
|
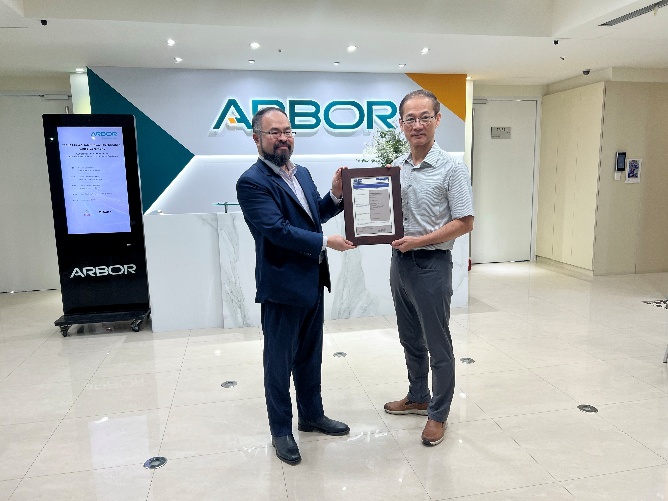
圖一:
左: 磐儀科技總經理連啟瑞
右: Bureau Veritas 資訊安全協理薛正
|
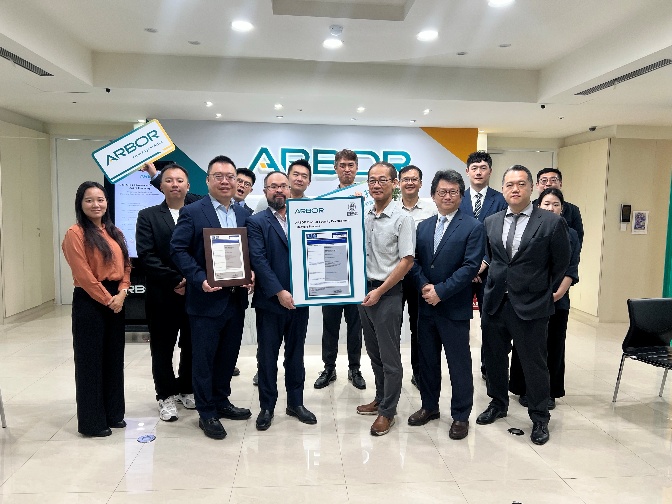
圖二:
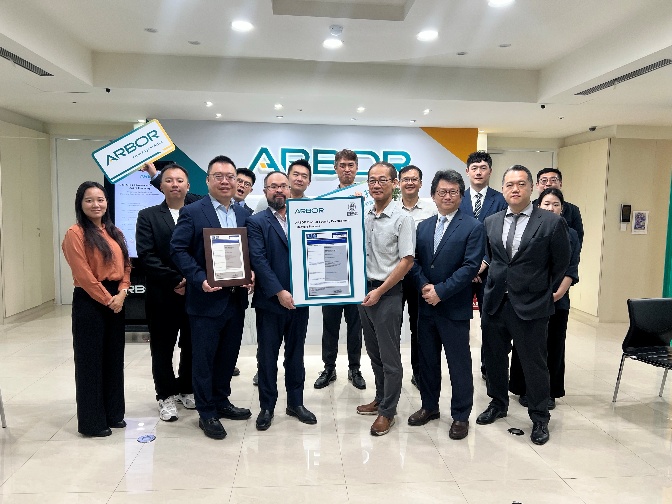
Bureau VeritasX 磐儀科技 X勤業眾信共同舉辦授證儀式
|
以 IEC 62443-4-1 國際標準建構安全產品開發生命週期
IEC 62443 為工業自動化與控制系統(Industrial Automation and Control Systems, IACS)重要的國際資安標準系列,其中 IEC 62443-4-1 聚焦於產品供應商的安全開發生命週期,涵蓋安全需求、安全設計、軟體開發、安全驗證與測試、資安缺陷管理,以及產品更新與維護等重要環節。
透過 IEC 62443-4-1 的導入,資安要求得以落實於產品生命週期各階段,從產品開發初期即納入安全考量,並透過制度化的開發與管理流程,持續提升產品的安全性與可靠性。
磐儀科技透過安全開發流程的建置,將資安要求進一步融入既有產品研發體系,強化從需求分析、設計、開發、驗證測試到後續維護的安全管理,逐步建構更完整的產品資安治理機制。
磐儀科技:資安是責任,更是給客戶的基本保障
無論客戶部署的是智慧工廠產線、邊緣運算節點,還是關鍵基礎設施中的工業電腦,都能因為磐儀在開發源頭就落實的資安管理機制,降低系統遭受入侵或攻擊的風險,讓客戶可以把心力專注在自己的營運與轉型上,而不是資安的後顧之憂。
磐儀科技總經理連啟瑞表示:「資安不應該是產品完成後才臨時加裝的防護,而應該是磐儀從第一天就承諾給客戶的責任。通過 IEC 62443-4-1 驗證,代表我們的開發流程已經通過國際標準檢驗,讓客戶在導入磐儀產品時,能夠更放心地把資安風險交給我們把關,專注在自己真正重要的營運目標上。」
勤業眾信:完善安全開發機制,提升產品安全事件應變與防禦能力
勤業眾信科技與轉型服務資深執行副總經理簡宏偉指出,隨著全球資安法規日趨嚴格,具備完善的風險評估與安全開發機制,已成為工控產業進入國際供應鏈的核心通行證。本次輔導安全開發流程導入,成功將需求分析、威脅建模、安全設計及測試驗證融入既有研發體系;並同步建立軟體物料清單(SBOM)與漏洞的定期追蹤與評估等機制。面對歐盟CRA即將於9月上路的製造商漏洞通報義務,企業可在既有4-1流程的堅實基礎上,進一步深化安全問題與安全更新管理,不僅能全面提升企業產品安全問題的應變與防禦能力、打造符合歐盟規範的產品安全架構,更能完美銜接歐盟法規要求。
Bureau Veritas:以國際驗證專業協助企業接軌全球市場
Bureau Veritas CPS 科技產品事業線台灣資訊安全協理薛正表示:「IEC 62443-4-1 證書的價值,不僅在於確認企業的安全開發流程符合國際標準,更重要的是協助企業將產品資安落實於研發與產品生命週期管理。隨著產品資安要求持續提升,建立符合國際標準且可持續執行的安全開發機制,將成為企業提升產品可信度及貼合國際資安法規要求的重要基礎,同時也將是提升企業國際市場競爭力的關鍵要素之一。」
Bureau Veritas and Deloitte Support ARBOR Technology in Achieving IEC 62443-4-1 Certification
Strengthening the Secure Product Development Lifecycle and Enhancing Global Cybersecurity Competitiveness
As industrial computers and edge computing devices continue to advance toward greater connectivity and intelligence, product cybersecurity is no longer limited to protecting individual functions or systems. Security considerations must be integrated throughout the entire product’s lifecycle from design and development to testing and ongoing maintenance. For manufacturers serving global markets, establishing cybersecurity mechanisms from the earliest stages of R&D and demonstrating secure development capabilities through internationally recognized standards have become essential to strengthening customer confidence and enhancing market competitiveness.
Bureau Veritas has completed the IEC 62443-4-1 Secure Product Development Lifecycle assessment for ARBOR Technology. ARBOR Technology has officially achieved IEC 62443-4-1 Maturity Level 2 (ML2) certification, demonstrating its continued commitment to strengthening product cybersecurity and secure development processes, while further enhancing its ability to meet global cybersecurity standards and market requirements.
|
|
|
|
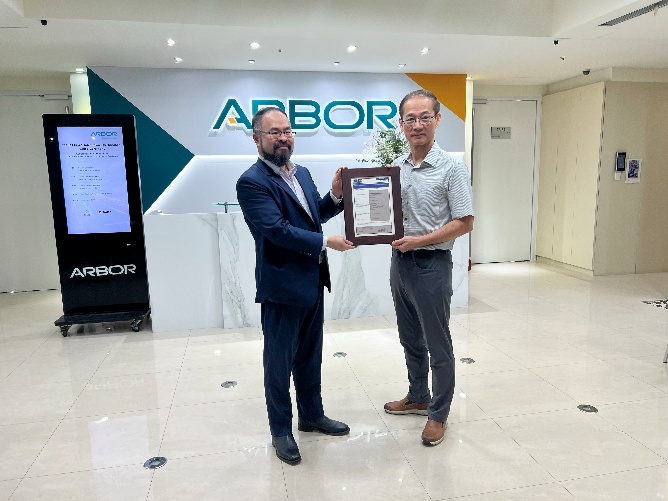
Photo 1
Left: Clark Lien, General Manager of ARBOR Technology receiving the certificate
Right: Bureau Veritas cybersecurity – David Hsueh
|
Photo 2
Bureau Veritas × ARBOR Technology × Deloitte jointly celebrate the certification achievement
|
Managing the Secure Product Development Lifecycle with IEC 62443-4-1
IEC 62443 is a key international cybersecurity standards series for Industrial Automation and Control Systems (IACS). IEC 62443-4-1 focuses on the secure development lifecycle of products supplied for use in IACS environments. It covers key areas including security requirements, secure design, secure implementation, security verification and validation, defect management, product updates, and ongoing maintenance.
By implementing IEC 62443-4-1, cybersecurity requirements can be systematically integrated into every stage of the product lifecycle. Security considerations are incorporated from the earliest stages of product development, while standardized development and management processes help continuously improve product security and reliability.
By embedding cybersecurity into its secure development processes, ARBOR Technology further integrates security requirements into its product R&D framework. This strengthens security management across requirements analysis, design, development, verification and testing, and subsequent maintenance, establishing a more comprehensive product cybersecurity governance framework.
ARBOR Technology: Cybersecurity Is a Responsibility and a Fundamental Commitment to Customers
ARBOR Technology stated that customers rely on the company’s extensive experience in industrial computing, and its solutions often serve as critical components of industrial infrastructure. Establishing a rigorous cybersecurity management framework during the development stage helps reduce the risk of cyberattacks after system deployment, allowing customers to focus on their core businesses rather than cybersecurity concerns.
ARBOR Technology’s General Manager, Clark Lien stated:
“Cybersecurity should not be an additional safeguard added only after a product is completed. It should be a responsibility undertaken from the very first day of development. Achieving IEC 62443-4-1 certification demonstrates that our development processes have been validated against international standards. When customers adopt ARBOR products, they can have greater confidence in entrusting cybersecurity considerations to us and focus on what matters most to their business.”
Deloitte: Establishing a Comprehensive Secure Development Framework to Strengthen Cybersecurity Incident Response and Defense Capabilities
Howard Jyan, the Partner of Technology & Transformation Service at Deloitte Taiwan noted that with increasingly stringent cybersecurity regulations, a comprehensive risk assessment and secure development framework has become a core requirement for industrial control systems entering international supply chains.
Through this engagement, cybersecurity requirements—including requirements analysis, threat modeling, secure design, and testing and verification—were successfully integrated into ARBOR Technology’s existing R&D framework. The project also established mechanisms for Software Bill of Materials (SBOM) management, vulnerability tracking, and periodic assessment.
With the EU Cyber Resilience Act (CRA) obligations for manufacturers expected to apply from September 2026, companies can build upon their existing IEC 62443-4-1 processes to further strengthen cybersecurity risk management throughout the product lifecycle. This will not only enhance products’ ability to prevent and respond to cybersecurity threats, but also help establish a cybersecurity framework aligned with European regulatory requirements and support compliance with evolving regulations.
Bureau Veritas: Leveraging International Certification Expertise to Support Global Market Expansion
David Hsueh, head of Cybersecurity sales, Bureau Veritas Consumer Products Services, Taiwan said: “The value of IEC 62443-4-1 goes beyond demonstrating that a company’s secure development processes comply with international standards. More importantly, it helps organizations embed product cybersecurity requirements into their R&D and product lifecycle management processes. As cybersecurity requirements continue to evolve, establishing a sustainable and continuously operating secure development framework will be a key foundation for enhancing product reliability, meeting international cybersecurity regulatory requirements, and strengthening competitiveness in global markets.”
This certification marks an important milestone in ARBOR Technology’s continued advancement of secure product development and demonstrates its commitment to integrating cybersecurity into its product development lifecycle.
Through its global expertise in testing, inspection and certification, Bureau Veritas remains committed to supporting organizations in addressing evolving cybersecurity requirements, strengthening product security and compliance, and building greater trust in an increasingly connected world.
|
 繁體中文
 English